XARA, a security flaw that Apple is already addressing
This isn't the first time an Apple app has been found to have flaws , and we've seen the glitches some of them have exhibited more than once. But this time, the problem that was observed was related to security, given the presence of malware that allowed access to various user data on the device. Apple named the threat XARA , derived from the acronym " Cross-App-Resource-Access ." The attack targeted both OS X and iOS devices.
The presence of XARA on computers created great controversy, as it intercepted data traffic between installed applications and could extract passwords and authentication keys. Recognizing the seriousness of the issue, Apple released a security update to protect all data shared within apps and block any application with configuration problems in the Mac App Store sandbox.
Apple releases update to fix XARA bug
Apple releases update to fix XARA bug
El discovery of this security flaw It was conducted at Indiana University, Georgia Tech and even across the globe at Peking University in China. All of these institutions reported the problem in October of last year. The company requested reports on the exploits for six months detailed in the publication.
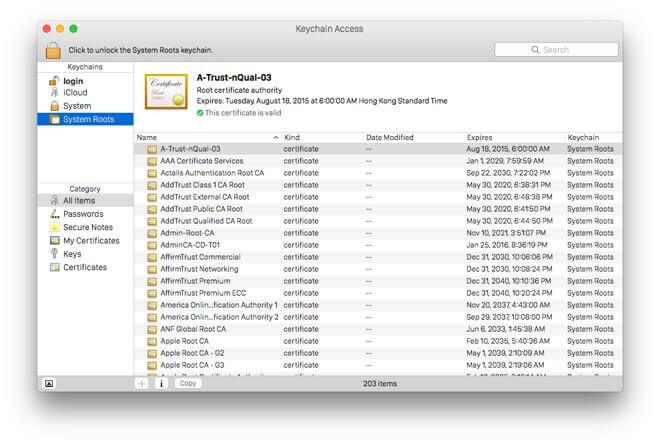
The document detailing the findings, published this week, explains that the reported malicious applications, in the case of OS X, were downloaded from the App Store , granting them access to the Keychain and Bundle IDs databases, the latter being an access control method. The other reported attacks targeted WebSockets and URL schemes.
Despite the existence of XARA , some media outlets have exaggerated its severity, highlighting a greater danger than it actually poses. Apple is working to eliminate this security flaw , but is also continuing to address all the details outlined in the report.